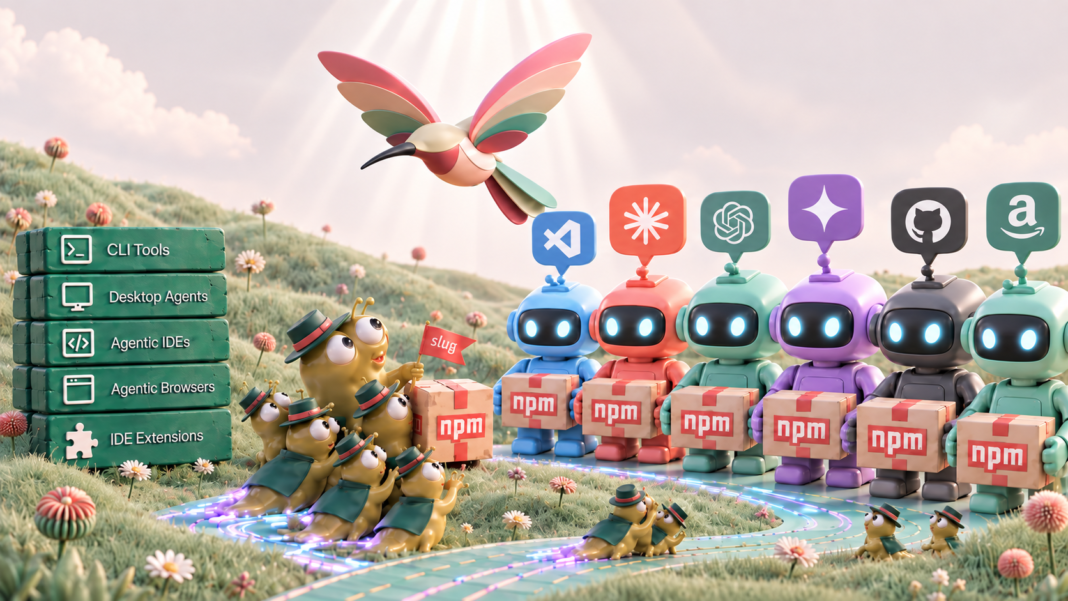

AI coding agents are increasingly capable of selecting dependencies, installing packages, and running code with limited human intervention. That convenience is changing the security profile of software development, as a new investigation from Bloom Security demonstrates: a weakness in package publishing can become more consequential when automated agents routinely pull software into development environments.
Bloom’s SlugFest research focused on npm Trusted Publishing, a system that allows authorized GitHub Actions workflows to publish packages through short-lived OpenID Connect (OIDC) credentials. The company found that a gap in repository identity verification could potentially allow an attacker to publish a malicious package under a legitimate name after reclaiming a GitHub repository slug.
The research began with an investigation into how AI agents acquire software dependencies, rather than with a search for a conventional credential-stealing attack.
A Growing Volume of Automated Installs
Bloom studied millions of AI agents across dozens of organizations to understand their package-installation behavior. Depending on the agent type, the company observed approximately 0.3 to 1.2 package installations per day. Developer machines installed roughly two to three packages per day through these agents.
Bloom also found that an average endpoint ran three agents, while developer machines ran five or more. Across its observations, an average endpoint received approximately 70 agent-installed packages per month, compared with nearly 350 on developer machines. These figures cover direct installations and exclude transitive dependencies.
Each additional package can introduce another source of code into a development environment. Package installation can also trigger lifecycle scripts, meaning a malicious release may have an opportunity to execute code without requiring a developer to manually launch the package itself.
Bloom reported that it caught and blocked one of its customers’ AI agents from attempting to install a vulnerable package. That incident helped illustrate how dependency-related risks can emerge through ordinary automated workflows.
How SlugFest Could Enable a Malicious Release
npm Trusted Publishing is designed to replace long-lived publishing tokens with temporary credentials issued through OIDC. In a correctly configured workflow, the registry checks whether the request comes from a trusted source.
Bloom found that npm’s initial trust binding could rely on a repository’s human-readable slug instead of immediately storing its immutable repository identifier. If a repository was renamed, transferred, or deleted before its first successful publication, its former name could potentially be claimed by another party.
An attacker could then create a repository using that name, configure a matching workflow, and request an OIDC token. Without the immutable identifier stored in the original trust relationship, npm could fail to distinguish the replacement repository from the one the package maintainer originally authorized.
Bloom demonstrated the publishing path using researcher-controlled repositories and an npm scope it controlled. The company’s analysis identified more than 1,500 packages with the relevant configuration, accounting for more than 10 million downloads.
These findings do not mean every AI agent or every npm package is vulnerable. Rather, they show how an underlying publishing weakness could intersect with automated dependency installation, creating a potential route from a compromised trust relationship to code execution in downstream environments.
Security Controls Must Account for Automated Behavior
For security teams, the challenge is not simply to block AI coding tools. It is to understand what those tools can install, which permissions they possess, and what happens when they introduce untrusted software into a development environment.
Bloom recommends auditing software used across the organization, including packages and other extensions or tools introduced through AI workflows. Teams should also consider supply chain controls that inspect or restrict software installation, alongside clear policies governing AI agent usage.
Package maintainers can take practical steps as well. Bloom advises using npm trust list to review publishing relationships, confirming that each repository slug still resolves to a repository under their control, and removing or recreating trust bindings after repository changes.
Following disclosure through GitHub’s HackerOne program on June 6, 2026, Bloom continued to track the issue and retested it before publication. The company found that npm had implemented a fix, which npm confirmed. Bloom also reported that npm’s GitLab Trusted Publishing implementation was affected.
AI agents are not the root cause of the vulnerability. They do, however, increase the importance of understanding how software enters development environments. As dependency management becomes more automated, security needs to cover not only who can publish a package, but also whether the publishing system verifies the right identity and whether downstream systems can safely consume the result.